Quick answer (updated November 6, 2026): Yes, according to the official Arena Breakout: Infinite team. On November 4, 2026 they posted that some CDN files used by the Level Infinite PC Launcher had been tampered with, that the issue affected "only a very small number of PC launcher environments", and that "Arena Breakout: Infinite is not affected, and you can continue playing as normal." The confirmed victim is the PC launcher of GODDESS OF VICTORY: NIKKE, whose launcher scripts were tampered with from September 27 and which, per the official timeline, started delivering malware to PCs on October 30 (a researcher documents agent activity from October 23) until the fix on November 4. If you only play ABI, there is no official advice to do anything. If you also launched the NIKKE PC launcher after September 27, 2026, check your PC now. The steps are below.
This guide covers what happened, the official timeline, why ABI players got worried, how to check a PC that also had NIKKE on it, and which "fixes" circulating on Reddit to ignore. It applies to Season 7: Utopia and the state of both official notices as of November 6, 2026.
What happened to the Level Infinite launcher?
Level Infinite, the Tencent publishing label behind NIKKE, confirmed on November 4 that "the PC Launcher's script files may have been tampered with by a third party" (statement on X, as quoted by BleepingComputer on November 5). The follow-up notice from the NIKKE Operations Team on November 5 gave the full chain:
- An open-source domain, insightjs.com, that "was used by certain game services" was hijacked by a third party on September 27, 2026.
- The same day, launcher script files were partially tampered with through that domain.
- From October 30, 2026, "distribution of malicious programs to users' PCs began through the compromised script."
- The anomaly was detected around midnight on November 4 (UTC+9) and the files were replaced in two waves that day.
An independent researcher who published the first technical write-up on GitHub found four modified JavaScript files on Level Infinite's CDN. Their analysis says the injected code pulled a remote-access agent onto the PC whenever the NIKKE launcher was open. While it ran, that agent could execute commands, read files and take screenshots. BleepingComputer examined two of the modified files and confirmed the obfuscated loader. It also found code in a related DLL sample that targets browser crypto-wallet extensions such as MetaMask and Phantom. It noted that "it is unknown whether the attackers deployed this additional component on infected systems."
One date is disputed. The official notice says malware distribution started on October 30. The researcher reports agent activity on infected machines from October 23. Treat the earlier date as the safe boundary if you are deciding whether to check your PC.

What did the Arena Breakout: Infinite team actually say?
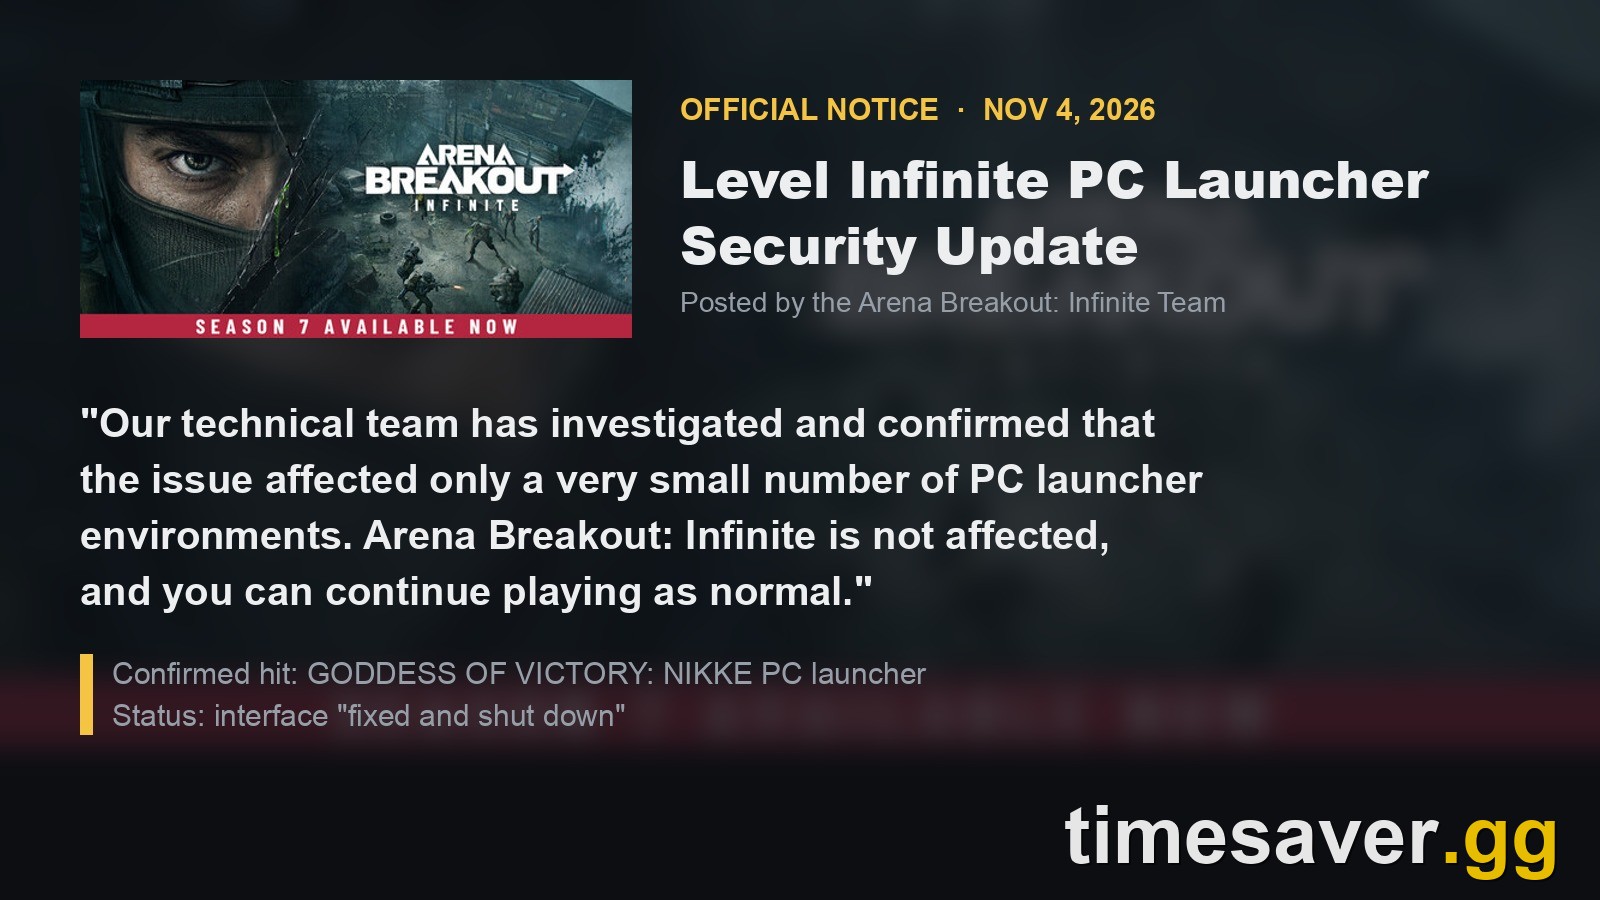
The ABI team posted a short notice titled "Notice: Level Infinite PC Launcher Security Update" to the official r/ArenaBreakoutInfinite subreddit on November 4, 2026. Here it is in full:
"Hi Operators, We recently identified a security issue in which some CDN files used by the Level Infinite PC Launcher were tampered with. Our technical team has investigated and confirmed that the issue affected only a very small number of PC launcher environments. Arena Breakout: Infinite is not affected, and you can continue playing as normal. The affected interface has now been fixed and shut down, and we will continue to strengthen the launcher's security." (The Arena Breakout: Infinite Team)
Three things in that statement matter:
- "Arena Breakout: Infinite is not affected" is a direct, unqualified claim. It is the only official position on ABI.
- "A very small number of PC launcher environments" confused a lot of players. In the Reddit thread, most readers took it to mean the NIKKE launcher, not ABI. One commenter disagreed with the "small number" part, saying everyone who opened the NIKKE PC launcher in the affected window was exposed. The NIKKE notice itself tells everyone who opened its Windows launcher after September 27 to run a check.
- "Fixed and shut down" refers to the tampered interface. The ABI notice gives no ABI-specific steps, because it says there is nothing to fix on the ABI side.
As of November 6, 2026 the ABI announcement has not appeared on the official Steam news feed for app 2073620. The latest Steam posts are the October 28 Halloween event and the October 28 Bans Notice. If Morefun posts a longer statement there, this guide will be updated.
Why were ABI players worried in the first place?
Arena Breakout: Infinite is a Morefun Studios game. On Steam, Morefun is credited as both developer and publisher. NIKKE is a Shift Up game published by Level Infinite. So why did a NIKKE breach light up r/ArenaBreakoutInfinite? The week's top threads give three reasons:
- Shared Tencent infrastructure. A highly upvoted thread argued that ABI "uses the same CDN as Nikke". That has not been confirmed. What is confirmed is that the ABI team felt the need to post a notice under the Level Infinite launcher name.
- Unexpected prompts. Several players reported their launcher asking for permission to run a command window, or antivirus software flagging a file. When a breach is in the news, every prompt looks suspicious.
- Researchers checking every Level Infinite title. One player said they found the same traces in their ABI files. When another player asked for specifics, the evidence pointed back to the NIKKE install. As of November 5, the GitHub write-up's own changelog says no other game's launcher is known to have loaded the malicious loader.
The short version: there is no public evidence that the ABI client or its launcher ever served the payload, and the developer says it did not. Most of the risk sits with players who have NIKKE installed alongside ABI.
How do you check your PC if you also play NIKKE?
If you opened the NIKKE Windows PC launcher at least once after September 27, 2026, 15:41 (UTC+9), the official notice tells you to check your PC. Do it in this order:
- Close every browser before you open the NIKKE launcher. From November 5, 2026, 08:00 (UTC+9), the official NIKKE PC client scans for the malware at launch. If it finds anything, a pop-up asks for permission to remove "the related logs, DLL files, and registry entries". The notice warns that DLL files can stay behind if a browser is still running.
- If you want proof before cleanup, save the evidence first. The researcher warns that the updated launcher's cleanup can delete the files that show whether the agent ever ran. They recommend running their read-only checker, or copying the launcher's Launcher\intl_service\debug.log file and the Launcher\log folder, before you open the launcher again. A line reading k2f_chan registered in that debug log means the agent ran on your machine.
- Run a full scan with up-to-date antivirus software. BleepingComputer recommends this for anyone potentially affected.
- If you were infected, treat the PC as compromised. BleepingComputer's advice is to reinstall Windows. Either way, change your passwords from a different, clean device. The NIKKE notice also says to revoke any API keys or access tokens you used on that PC.
- Report losses to NIKKE customer support. The notice says Level Infinite will review "each inquiry carefully" for damage to external accounts and finances.
If you only play ABI, the developer's position is that none of this applies to you. You can still run a normal antivirus scan. It costs nothing and it settles the question.
Which "fixes" should you ignore?
A breach like this attracts bad advice and outright scams. Here is what to skip:
- Commands pasted by strangers. The GitHub write-up specifically flagged a fake cleanup command posted in its own comments. Never paste a PowerShell or Command Prompt line from a Reddit or Discord comment into an admin terminal. Use the official in-client check, your antivirus, or the researcher's published tool.
- "Download the patched launcher here" links. Only reinstall ABI from Steam (app 2073620), the Epic Games Store, or the official site at arenabreakoutinfinite.com. ABI has been on Steam and Epic since its 1.0 launch on September 15, 2025.
- Account-recovery or "ban appeal" services that show up in DMs during the panic. They are a separate scam. A real ban or lockout goes through Morefun's own support. See our 10-year ban and appeal explainer for how that process works.
- Uninstalling ABI "just in case". It does not help if the developer is right, and it does not help if they are wrong either, because the reported payload's persistence does not depend on the game being installed. Scan the PC instead.
What about the "launcher wants to run cmd" prompt?
This was one of the most-asked questions of the week. Neither official notice mentions a command-window prompt in the ABI launcher, and there is no confirmed link between that prompt and the NIKKE malware. Keep it simple:
- If Windows User Account Control asks for permission and you did not just click something that needs it, choose No. Then check the publisher name shown in the dialog.
- Restart the launcher from Steam or Epic. If the prompt comes back, run an antivirus scan before you accept it.
- If you use the DMA Guard security feature, follow the official BIOS steps in our DMA Guard, VT-d and IOMMU fix guide rather than random tweaks. Never disable anti-cheat or security components to "fix" a prompt. Morefun's official ban announcements name "abnormal launcher environments" among the signals behind cheating penalties.
Does this affect your ABI account, Koen or stash?
There is no official statement that any ABI account, stash or Koen balance was touched, and the ABI team says the game was not affected. Your stash, Koen, level and Bonds carry on as normal through Season 7. ABI does not wipe stashes between seasons; see does Arena Breakout: Infinite wipe. If you used the same password for your game account and an account you logged into on an infected NIKKE PC, change it anyway.
One more warning that fits here. Breaches are a favourite excuse for "your account was hacked, buy Koen to recover your losses" pitches. Morefun penalises Koen buyers as well as sellers. Penalties include confiscation and escalating bans up to ten years, and the October 28 Bans Notice is the latest of its fortnightly reports. Do not let a security scare push you into a trade that gets you banned for real.
Key numbers at a glance
| Item | Value | Source |
|---|---|---|
| Tampered files on the Level Infinite CDN | 4 JavaScript files | Independent GitHub analysis, confirmed in part by BleepingComputer |
| Script tampering began | September 27, 2026, 15:41 (UTC+9) | NIKKE official notice |
| Malware distribution began | October 30, 2026 (official) / October 23 (researcher) | NIKKE notice / GitHub analysis |
| Last file's CDN cache refresh completed (gradual rollout followed) | November 4, 2026, 12:09 (UTC+9) | NIKKE official notice |
| In-client malware scan live | November 5, 2026, 08:00 (UTC+9) | NIKKE official notice |
| ABI affected? | "Not affected" | ABI team notice, November 4, 2026 |
FAQ
Is the Arena Breakout: Infinite launcher safe to open right now? According to the ABI team's November 4, 2026 notice, yes: "Arena Breakout: Infinite is not affected, and you can continue playing as normal." The confirmed compromise was in the NIKKE PC launcher.
Did Arena Breakout: Infinite get hacked? No ABI breach has been confirmed. The tampered files belonged to the Level Infinite PC launcher used by NIKKE, and the ABI developer says ABI was not affected. Reddit claims that ABI shares the same CDN have not been confirmed by any official source.
I play both ABI and NIKKE. What should I do? If you opened the NIKKE Windows launcher after September 27, 2026, follow the NIKKE security check. Close all browsers, let the updated NIKKE client scan at launch, run a full antivirus scan, and change passwords from a clean device. Save the launcher's debug log first if you want proof of whether the agent ran.
What does "k2f_chan registered" mean? That line in the NIKKE launcher's Launcher\intl_service\debug.log file is the indicator the researcher and BleepingComputer cite as proof the malicious agent ran on that PC. It does not prove the extra crypto-stealing DLL was installed. Treat the machine as compromised either way.
Should I uninstall Arena Breakout: Infinite? There is no official advice to. Uninstalling the game does not remove anything the reported malware may have installed elsewhere. A full antivirus scan is the useful step, and for an infected NIKKE PC, a Windows reinstall.
Will Morefun compensate ABI players? No ABI compensation has been announced, which fits with the statement that ABI was not affected. NIKKE has announced in-game compensation for its own players.
Want more Arena Breakout: Infinite guides? Every page is checked against Morefun's official Steam announcements and dated to the current season.